Introduction to Cosmonic
Cosmonic gives you the tools to sandbox workloads like AI agents, the tools they use, and the code they write. Run sandboxes on any machine, from your laptop to your cluster, at massive density.
Each sandbox is a WebAssembly component that starts with no access to anything and gets only the files, hosts, and credentials its job needs. These sandboxes are small enough to give one to everything, and to run them by the million.
In this documentation, you'll learn how to:
- Build sandboxed agents with the open source Cosmonic Agent SDK.
- Build and run sandboxes on your own machine with Cosmonic Desktop, now in public beta.
- Run sandboxes at scale on Kubernetes with Cosmonic Control.
What is the Cosmonic Agent SDK?
The Cosmonic Agent SDK is a set of open interfaces, cosmonic:agent, for building agents composed of secure, isolated, deny-by-default sandboxes. The agent's loop, each tool and its conversation are separate parts. The host makes the model calls and holds the keys, so a key never enters the agent, and it keeps every session outside the agent, so a session survives a crash, a restart or a move to another machine. Agents built on the SDK run on Desktop and on Control without changes.
- Get to know the Agent SDK and how its parts fit together.
- Quickstart: build your first agent.
- Write a typed tool: build a tool an agent can call.
What is Cosmonic Desktop?
Cosmonic Desktop runs sandboxed agents, tools and apps on your own machine. It's a free app for macOS, Windows and Linux, now in public beta, with no cloud required. Its Agents page runs agents in the sandbox, each tool with its own grant, and it runs AI-generated code and MCP servers the same way.
Desktop shows you exactly what each sandbox can reach before it runs, and runs it with nothing but the access you granted. Coding agents like Claude Code and OpenAI Codex can connect through the built-in MCP server to build and deploy into your local sandbox. When you're ready to ship, the same components deploy to Cosmonic Control, and the boundary you trusted on your laptop is the boundary that runs in production.
- Run an agent in a sandbox, with each tool granted only what it needs.
- Get started with Cosmonic Desktop and run your first sandboxed workload.
- Connect your coding agent so it can build and run code in the sandbox.
- Sandbox an MCP server and see what it can reach before it runs.
What is Cosmonic Control?
Cosmonic Control is a Kubernetes-native control plane for securely running agents and tools, MCP servers, microservices, and other sensitive or untrusted code in sandboxed WebAssembly components. Ultra-dense workloads deploy on any cloud or edge, including your own on-premises and air-gapped environments. Each workload reaches only what it was granted, which limits what a tricked agent, a compromised dependency or a remote code execution bug can do.
Built on the Incubating CNCF project wasmCloud, Cosmonic Control helps platform engineering teams cut costs by scaling to zero and maximizing node density, while providing enterprise-grade security for agents, functions, and other code, and integrating with the cloud-native tooling you already run.
- To try it out, get started for free.
- If you're running agents, see Run an agent on Cosmonic Control.
- If you're an operator, explore the Architecture and Operations documentation, and secure your cluster.
- If you're a developer building components, see the Template Catalog and the wasmCloud Developer Guide.
How does it work?
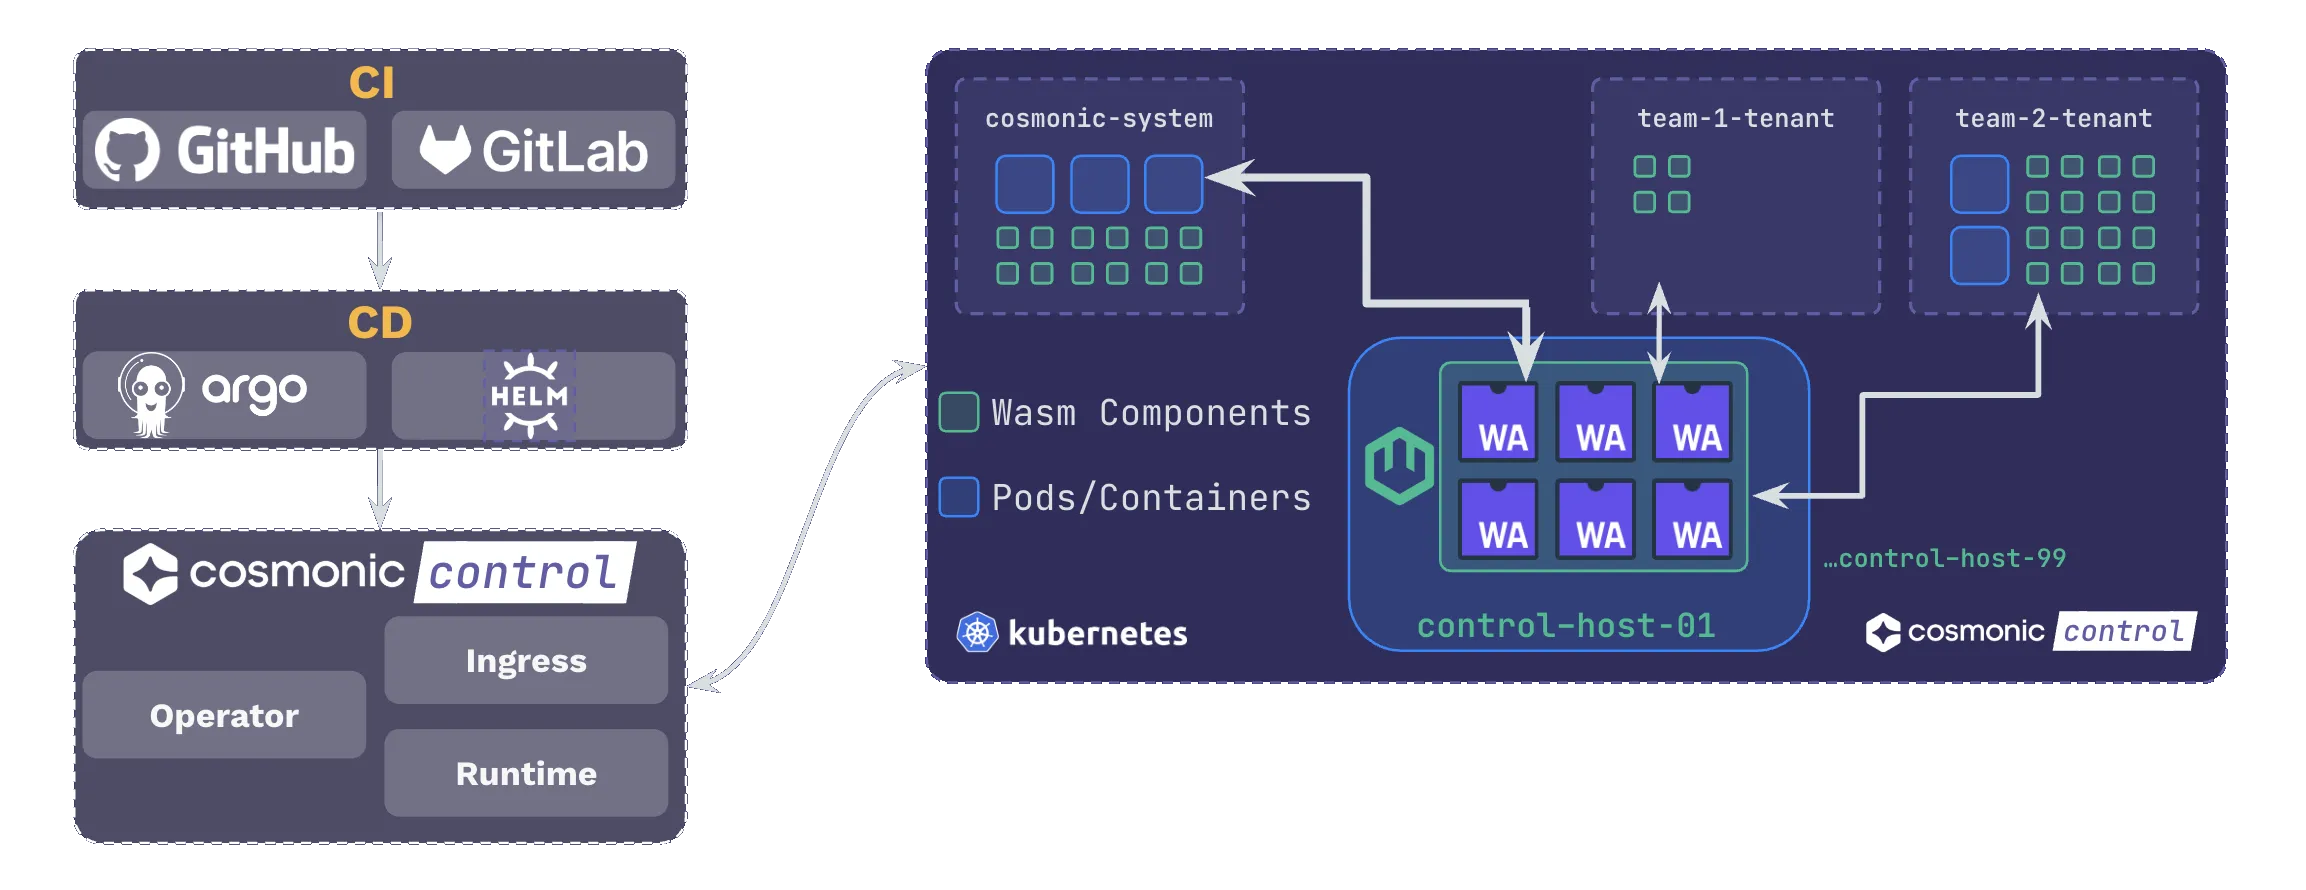
- Teams compile code to WebAssembly component sandboxes, using open source tooling and streamlined pipelines for builds, attestation, and publication.
- Workloads deploy declaratively with any GitOps.
- Sandboxed workloads run on Cosmonic Control hosts, with traffic routed through the built-in ingress proxy.
The same capability-bounded component runs in both products, agents included, so what you develop and sandbox on Cosmonic Desktop is what deploys to Cosmonic Control. For more, see the Architecture documentation and From Laptop to Cluster.
Join the community
We're proud members of the wasmCloud community. Join us on the wasmCloud Slack or in the weekly wasmCloud community meeting.